

 Newsletters


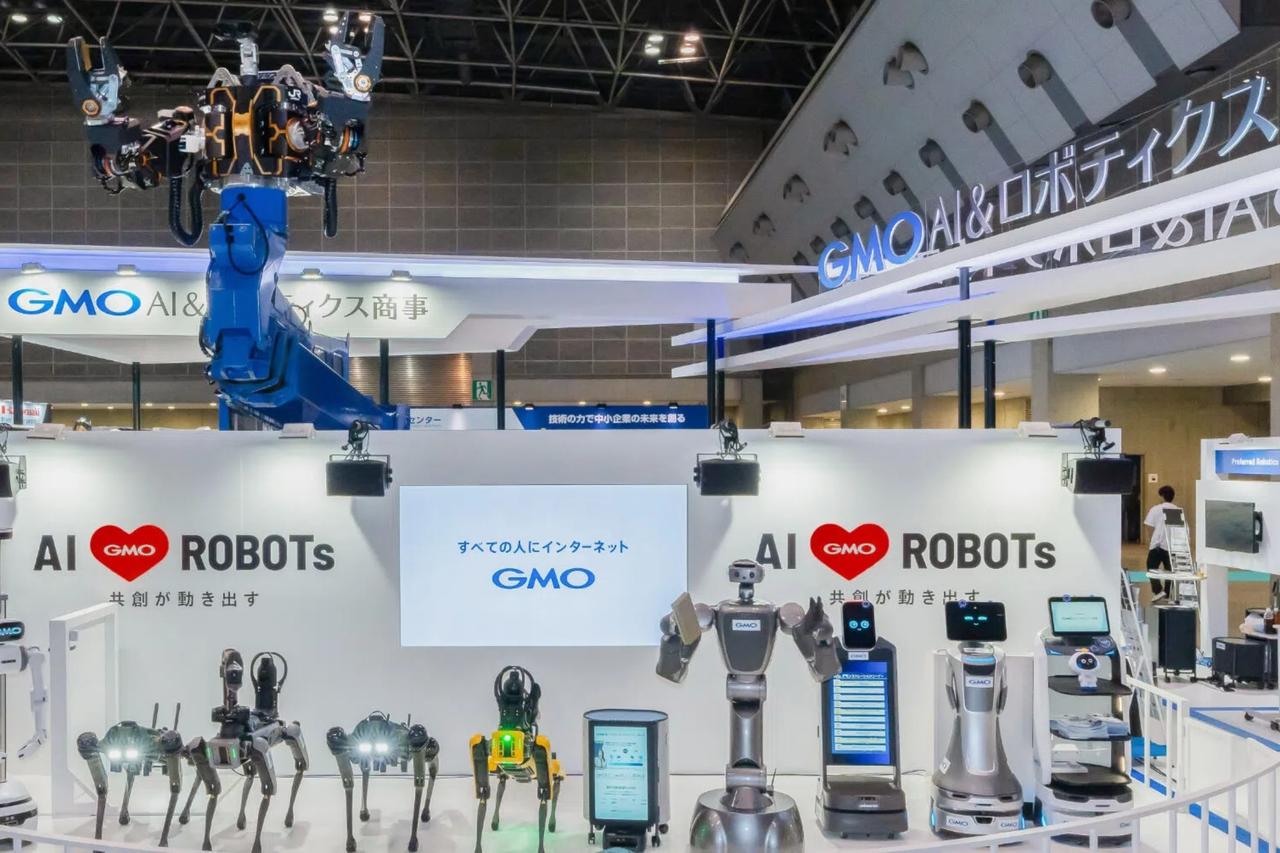


Japanese internet services firm GMO Research & AI Inc. said Tuesday that hackers stole data of up to 948,500 members after gaining unauthorized access to its server, according to local media.
Kyodo News reported that the compromised information included names, email and home addresses, phone numbers and encrypted passwords. The company also said members' reward points worth about 2.9 million yen ($18,000) were fraudulently swapped for Amazon gift card codes. Members earn the points by completing surveys on the company's infoQ website.
The attack began Friday, when hackers exploited a vulnerability in software used by the site. GMO detected the breach Saturday, blocked the unauthorized access, and suspended the service. The company said it would fully reimburse affected users, and a cybersecurity firm is helping with the investigation.
In a separate case, discount store chain operator Mr Max Holdings Ltd. said Tuesday that personal information of up to 1.7 million customers may have been exposed after unauthorized access to a server used for its app and online store.
According to Kyodo, the potentially exposed data included names, email addresses and phone numbers, but not credit card details, home addresses or dates of birth.
Mr Max detected the breach Saturday and immediately suspended the affected services. The retailer said it had found no evidence of misuse but urged customers to stay alert for phishing emails, which are fraudulent messages designed to steal personal information.
The incidents come amid a series of major data breaches in Japan. Monogatari Corp., operator of the Yakiniku King barbecue chain, said Monday that more than 10 million pieces of customer information were leaked after unauthorized access to its reservation and rewards app.
Daiwa Securities Group also said data belonging to about 110,000 customers may have been compromised after unauthorized access to a server run by a contractor.


 Set as preferred source
 Set as preferred source

 1 min read
 1 min read


