Newsletters




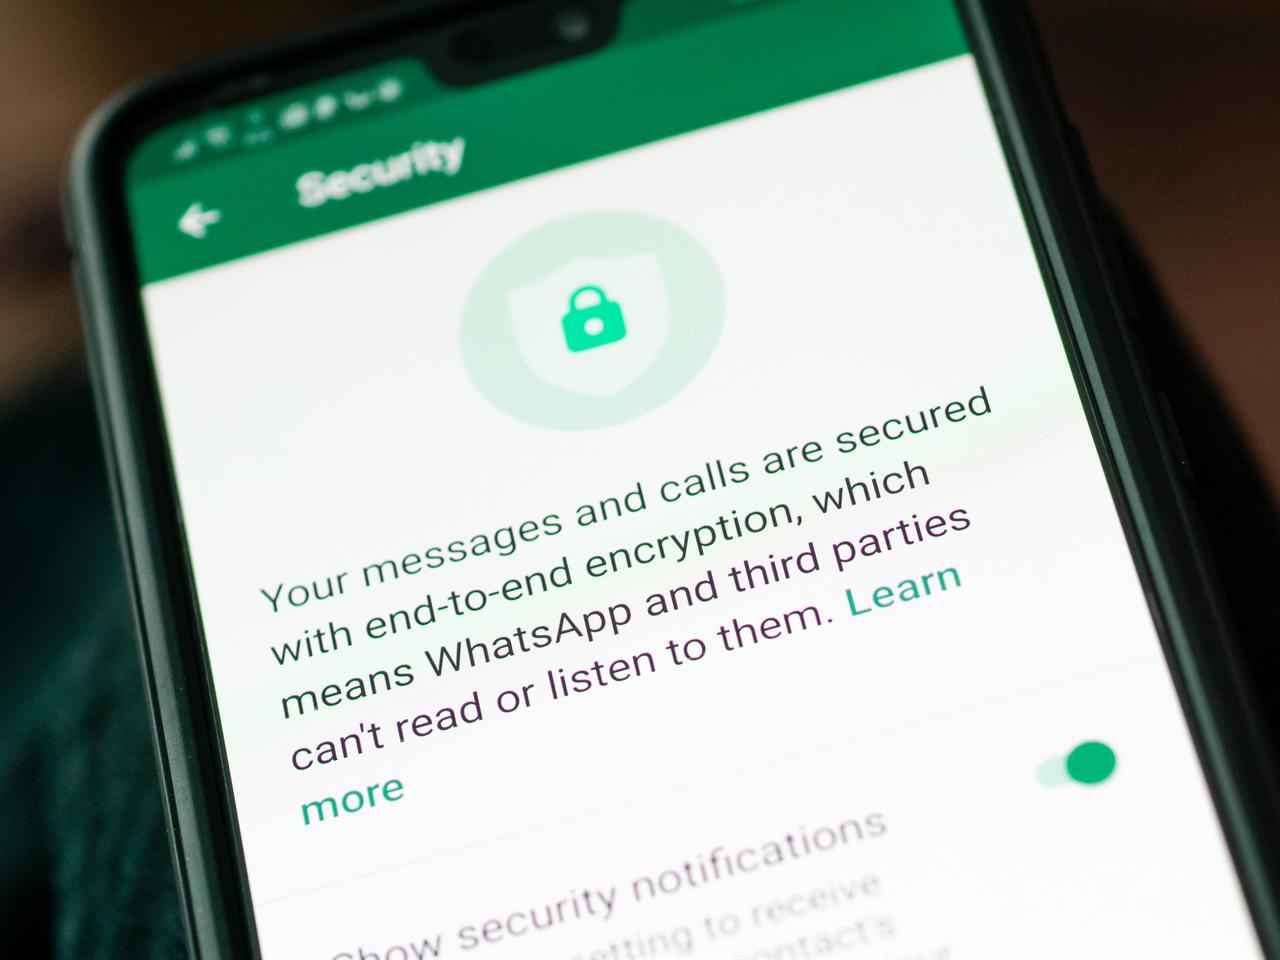
Experts in Türkiye are urging smartphone users to keep operating systems and apps updated as complaints about hijacked messaging accounts and related fraud attempts increase.
Ibrahim Gunduzgil, head of the Cybersecurity Program at the Vocational School of Istanbul Commerce University, told Anadolu Agency (AA) that users should never share verification codes received by SMS or through an app.
“Phone operating systems and the applications in use must be updated regularly,” Gunduzgil said. “Updates do not only offer new features. They are very important for fixing identified security vulnerabilities.”
Cyberattacks targeting iPhone users and the popular messaging app WhatsApp in Türkiye and worldwide are being used to break into personal accounts and analyze past conversations. The spyware closely follows the victim’s conversation style. The victim's contacts then receive messages asking for an “urgent loan” to be sent via IBAN bank transfer.
Gunduzgil added that such attacks are not limited to WhatsApp. Other methods can take over accounts or active sessions on Telegram and similar apps.
Gunduzgil said attackers generally rely on fake links, phishing, and social engineering. He advised users to turn on extra protection such as two-step verification, check linked devices and active sessions in each app, and end access for any unrecognized device. For money requests from familiar contacts, confirm the sender’s identity through a different channel.
Android and iOS users can both be targeted, Gunduzgil said. He noted that recent applications to his team came mostly from iOS users whose WhatsApp accounts were hijacked.
“In our studies, the problem appears to come from devices where the iOS update has not been or is not being installed,” he said.
Gunduzgil also pointed to risks from WhatsApp Web, Telegram Desktop and similar tools that allow computer access to accounts.
Sessions left open on untrusted computers, malware and fake QR codes can lead to unauthorized access.
“The user may keep using the app normally on the phone while the attacker accesses the account from another device. The user may not notice this,” he said.

Sabri Erdemir, head of the Computer Programming Program at the same school, said the user should keep digital evidence.
This includes screenshots of suspicious messages, links, phone numbers, bank account details, transfer receipts and the date and time of the incident.
Erdemir said disconnecting a device from the internet may limit an attacker’s ongoing access and help preserve evidence if remote access is suspected.
If possible, the device should not be reset and apps should not be deleted, he said, as this could erase existing records.
Anyone who suffers a financial loss should contact their bank immediately, report the suspicious transaction and request that the transfer be stopped or reversed.
Erdemir also advised victims to report the incident to the Chief Public Prosecutor’s Office, police, or gendarmerie, even without financial loss, since hijacked accounts can later be used for other fraud.
Erdemir said criminal liability rests with those who carry out and take part in the unlawful act, and that having an account hijacked does not make its owner responsible for fraud.
Digital forensics and criminal investigations can examine access and session records, IP addresses, device data, bank activity and transfers, he said. An IP address or bank account alone does not conclusively identify the perpetrator, he noted.
“Although attackers may use different techniques to hide their identities, it is possible to identify perpetrators by correlating the appropriate digital evidence,” Erdemir said.


 Set as preferred source
 Set as preferred source

 3 min read